
近期歐洲多國接連傳出針對冷藏系統的網路攻擊災情,超市冷凍櫃與冰箱溫度被遠端調高,導致大量生鮮食物變質報廢,部分醫院血庫也遭波及,血液製品因溫度異常面臨風險,引發對民生與醫療供應鏈安全的高度關注。
The U.S. and France suspect Iran is responsible for the cyberattack on European supermarket refrigerators and freezers that caused tens of millions of dollars of damage in spoiled food and equipment. https://t.co/d5IHNnMeON
— The Wall Street Journal (@WSJ) November 9, 2026
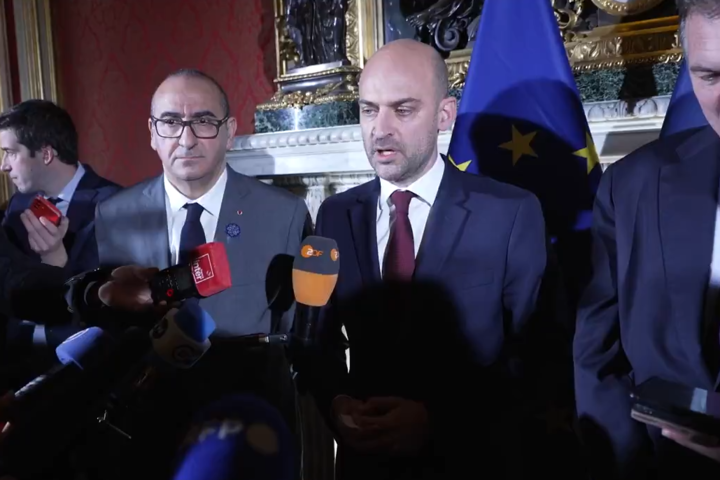
綜合法新社與《英國廣播公司》(BBC)報導,法國周一(9日)指控伊朗伊斯蘭革命衛隊(IRGC)旗下網路單位,是近期針對超市冷藏系統發動大規模網路攻擊的幕後黑手,並已展開調查、傳喚伊朗大使,同時尋求歐盟層級制裁。
法國外交部長巴羅(Jean-Noel Barrot)表示,10月11日至12日發生的攻擊「侵略程度前所未有」,他確認「這起攻擊是由伊朗伊斯蘭共和國伊斯蘭革命衛隊所發動」,「這是首次在法國境內為破壞目的而發動的大規模網路攻擊。它對國家利益與法國人民安全構成重大攻擊。因此絕不會沒有回應」。他補充,將採取「相稱且必要」的公開或私下措施回應並嚇阻類似行為。
Les 11 et 12 octobre, près de 700 sites de distribution ont été touchés par une campagne cyber d'une ampleur et d’une agressivité inédites. Aujourd’hui, grâce au travail des services de l’Etat, nous connaissons les responsables : les Gardiens de la Révolution de la République Islamique d'Iran. L'ambassadeur d'Iran a été convoqué. Nous allons sanctionner les auteurs et prendre toutes mesures que nous jugeons nécessaires et proportionnées pour répondre à ces attaques et dissuader ceux qui songeraient à les reproduire.
— Jean-Noël Barrot (@jnbarrot) November 9, 2026
巴黎檢方已針對伊朗革命衛隊旗下攻擊性網路單位「沙希德·卡維」(Shahid Kaveh)的領導人及其2名副手申請國際逮捕令。調查人員發現,攻擊者使用波斯語,且IP位址與伊朗裝置有關。駭客取得冷藏系統網路存取權後,將溫度遠端調高至攝氏50度,造成大量食物變質與設備損壞,部分案例甚至引發火災。
受影響的連鎖超市包括家樂福(Carrefour)、E-Leclerc、Intermarché、Monoprix與Coopérative U,其中Intermarché至少300家門市遭波及,Coopérative U超過100家,家樂福約80家,Monoprix約5%門市受影響,零售商估計損失達數百萬歐元。
除法國外,比利時、愛沙尼亞、愛爾蘭、盧森堡與瑞典等地超市也在11月2日通報類似冷藏溫度異常飆升現象,數十家門市與一處食品配送中心受影響。近期歐洲多國還傳出醫院血庫冷藏系統遭類似手法干擾的災情,導致部分血液製品因溫度異常而面臨報廢風險,進一步凸顯攻擊對民生與醫療供應鏈的潛在威脅。
The @FBI and our partners are seeing malicious cyber activity targeting industrial refrigeration and cold-chain monitoring systems around the world. These systems help keep food, medicine, and other products at safe temperatures and are widely used across critical infrastructure sectors. Attackers are targeting electronic temperature and refrigeration controllers, particularly in grocery stores and cold storage facilities. In at least one recent incident, attackers targeted refrigeration components at three foreign blood service facilities. While this attack was unsuccessful due to the proper alert mechanisms in place, security weaknesses in unpatched or internet-accessible controllers can allow attackers to change system settings, potentially causing inventory loss and equipment damage. The FBI urges organizations using these systems to take the following steps: ➡️ Take controllers off the public internet ➡️ Put access behind a firewall ➡️ Change default passwords ➡️ Learn how vendors configure devices ➡️ Set safe temperature limits ➡️ Ensure alerts reach the right contacts For technical details and more information on how to protect these systems, read our advisory: https://t.co/706NrSgXIp
— FBI Cyber Branch (@FBICyberBranch) November 5, 2026
上周,美國聯邦調查局(FBI)網路犯罪部門在社群平台上發表聲明稱,他們正與合作夥伴一起「針對全球工業製冷和冷鏈監控系統的惡意網路活動」,並指出「未經補強或可通過互聯網訪問的控制器中的安全漏洞可能允許攻擊者更改系統設置,從而造成庫存損失和設備損壞」。
FBI敦促所有依賴此類系統的組織將其控制器「從公共網路移除」,並將對系統的訪問限制在防火牆之後,此外還應採取其他安全措施。
網路安全專家指出,因國際合作有限且攻擊者透過多國節點中繼,要精準追蹤特定團體仍相當困難。